Artificial intelligence is transforming the digital world, but its rapid development is also creating serious cybersecurity challenges. Criminal hackers are increasingly using advanced AI tools to automate attacks, identify weaknesses and steal sensitive information.
A growing concern among security experts is that these technologies are making sophisticated cyberattacks easier to organize. Attackers no longer need to perform every step manually. Instead, AI-powered systems can help them investigate targets, identify vulnerabilities and coordinate multiple stages of an intrusion.
A recent warning involving former FBI counterterrorism unit chief Bassem Youseff has brought renewed attention to the issue. Speaking about the growing threat of AI-assisted hacking, Youseff warned that artificial intelligence could significantly increase the speed and scale of cyberattacks.
His concerns come as federal authorities and private cybersecurity researchers report increased misuse of autonomous AI frameworks.
The warning raises an important question: Are businesses, government agencies and ordinary internet users prepared for a new generation of automated cybercrime?
Retired FBI Official Raises Concerns About AI Cyber Threats
Artificial intelligence has become an important part of modern cybersecurity. Companies use AI to detect suspicious activity, investigate security incidents and protect sensitive information.
However, the same technology can also benefit criminals.
Youseff’s warning highlights how quickly malicious actors can adopt new tools. Hackers can use AI to accelerate activities that previously required significant technical knowledge and human effort.
According to reporting by Just the News, Youseff discussed the growing danger of AI-powered attacks and the potential consequences for American infrastructure.
He compared the increased capabilities to earlier denial-of-service attacks, explaining that artificial intelligence could make such threats faster and more powerful.
Just The News
The concern is not limited to one type of cybercrime.
AI can support several stages of an attack, including:
Identifying vulnerable computer systems.
Creating convincing phishing messages.
Automating password and credential attacks.
Developing or modifying malicious code.
Searching compromised networks for valuable information.
Supporting large-scale operations against multiple targets.
These capabilities could allow criminal groups to conduct more attacks with fewer resources.
FBI Warns That Hackers Are Weaponizing AI Tools
The Federal Bureau of Investigation has repeatedly warned that cybercriminals are exploiting artificial intelligence.
In a 2023 cybersecurity summit, former FBI Director Christopher Wray discussed how malicious actors could use generative AI to create deepfakes and malicious code.
He also highlighted a case involving a darknet user who allegedly used a generative AI program to develop malware and share instructions with other criminals.
Wray warned that AI could help attackers develop increasingly sophisticated and customizable capabilities.
FBI+1
More recent developments suggest that the threat is becoming increasingly automated.
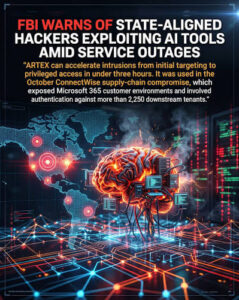
In November 2026, the FBI warned organizations about ARTEX, an AI-powered penetration-testing framework that attackers have reportedly repurposed for malicious operations.
The framework was originally designed around security testing. However, criminals have used its capabilities to automate cyber intrusions.
The FBI reported that some intrusions progressed from initial targeting to privileged access in less than three hours.
This is particularly concerning because attackers can coordinate multiple operations while requiring relatively little human involvement.
Inc.com+1
ARTEX: The AI Framework Raising Cybersecurity Concerns
One of the most significant developments in the current AI cybersecurity debate is the reported misuse of ARTEX.
The framework demonstrates how artificial intelligence can coordinate different security tools and execute complex tasks.
Rather than manually performing every operation, an attacker can provide a high-level objective. AI agents can then help translate that objective into individual actions.
These actions may involve reconnaissance, vulnerability discovery, security testing and attempts to gain access to computer systems.
The danger comes from the combination of automation and access to existing cybersecurity tools.
How ARTEX Can Accelerate Cyberattacks
Traditional cyberattacks often require attackers to move through several stages.
They may first investigate a target, identify weaknesses and test possible entry points. Once they gain access, they may attempt to increase their privileges or locate valuable information.
AI-powered frameworks can accelerate parts of this process.
For example, automated agents can help:
Examine internet-facing applications.
Identify potentially vulnerable services.
Coordinate existing security tools.
Investigate weaknesses in connected systems.
Search for exposed credentials.
Support further activity after an initial compromise.
The FBI’s warning suggests that these capabilities can significantly reduce the time required to conduct an intrusion.
The framework does not need to invent entirely new hacking techniques to become dangerous. Automating existing techniques can already create a substantial advantage for attackers.
cybersecuritydive.com+1
Why Criminals Are Interested in AI Automation
Speed is one of the biggest advantages AI offers cybercriminals.
A human attacker may need considerable time to examine a large network. Automated agents can process information and perform repetitive tasks much faster.
AI also makes it easier to conduct multiple operations simultaneously.
This could increase the number of potential victims targeted by a single criminal group.
Another concern is accessibility. People with limited technical knowledge may be able to misuse advanced tools that previously required specialist skills.
However, automation does not make every attack successful. Security weaknesses, system configurations and defensive monitoring still influence the outcome.
AI Cyberattacks Could Target Banks, Hospitals and Government Agencies
The growing use of AI in cybercrime creates risks for organizations that manage sensitive information or essential services.
Banks, hospitals, government departments and telecommunications providers are particularly important targets because they operate systems that millions of people depend on.
Financial Institutions Face Growing Risks
Banks store valuable personal and financial information.
Cybercriminals may attempt to steal login credentials, access customer databases or compromise payment systems.
AI can make phishing campaigns more convincing by helping criminals produce realistic messages that imitate financial institutions.
Attackers may also use automation to investigate exposed services and search for weaknesses in digital banking infrastructure.
A November 2026 report by The Register described ARTEX-related campaigns involving credential theft and attempts to misuse AI services.
The reporting also highlighted attempts to use AI-generated deepfake videos to bypass identity verification systems at cryptocurrency exchanges.
theregister
Hospitals Could Face Disruptive Attacks
Healthcare organizations depend on digital systems to manage patient records, appointments, medical devices and administrative operations.
A successful cyberattack could interrupt access to important information.
Ransomware attacks are particularly concerning because criminals may attempt to lock critical files and demand payment.
AI-assisted attacks could increase the speed at which criminals identify exposed systems and investigate potential entry points.
Hospitals therefore need strong backup systems, secure access controls and effective incident response plans.
Government Infrastructure Remains a Major Concern
Government agencies manage sensitive records and operate services that are essential to national security.
These systems may contain information about citizens, public administration, law enforcement and national infrastructure.
In August 2026, reporting on a joint warning from US federal agencies highlighted threats involving AI-assisted development of exploit scripts targeting industrial control systems.
The warning identified risks involving programmable logic controllers used in sectors such as energy, water and agriculture.
The Record from Recorded Future News
Such developments demonstrate why cybersecurity is not simply a technology issue. It is also a matter of public safety and national resilience.
AI Is Making Phishing and Online Scams More Convincing
Not every cyberattack involves sophisticated software or complicated technical operations.
Many criminals continue to rely on social engineering, which involves manipulating people into revealing information or approving unauthorized actions.
Artificial intelligence can make these scams more effective.
AI-Generated Phishing Messages
Traditional phishing messages often contain spelling mistakes, unusual wording or suspicious formatting.
AI tools can help criminals produce more professional messages.
They can imitate the communication style of banks, employers, government agencies and popular online services.
A convincing message may encourage someone to click a fraudulent link, download a malicious attachment or provide account information.
Deepfake Voice and Video Scams
Deepfake technology creates artificial images, voices and videos that imitate real people.
Criminals may use these tools to impersonate company executives, relatives or public figures.
For example, an employee might receive a fake voice message that appears to come from a senior manager requesting an urgent financial transfer.
These scams can be difficult to recognize because they exploit trust rather than relying entirely on technical weaknesses.
Automated Attacks at Greater Scale
AI can also help criminals personalize messages for different victims.
Instead of sending identical messages to thousands of people, attackers may create communications that appear relevant to individual recipients.
This can make fraudulent messages more believable.
Users should therefore avoid treating professional language, familiar voices or realistic videos as proof that a communication is genuine.
Google and Cybersecurity Researchers Warn of an AI Hacking Shift
The concerns raised by former FBI officials are also reflected in recent research from major technology and cybersecurity companies.
Google’s Threat Intelligence Group reported in November 2026 that malicious actors are increasingly moving beyond basic AI prompting toward autonomous, multi-agent systems.
These systems can coordinate different tasks during a cyber operation.
Google described the changing threat landscape as a critical turning point. Researchers also identified the misuse of several AI-enabled penetration-testing frameworks, including ARTEX, CyberStrikeAI, HexStrike AI and PentAGI.
cybersecuritydive.com
This development matters because attackers can combine different tools rather than depend on one application.
For example, one system might help identify weaknesses while another analyzes information or supports additional operations.
The result could be a more coordinated attack.
AI Is Lowering the Technical Barrier
Cybercrime has traditionally required different levels of technical expertise.
Experienced hackers often understand networking, operating systems, programming and security vulnerabilities.
However, AI assistants can simplify some technical tasks.
They can explain unfamiliar concepts, help analyze errors and automate repetitive work.
This creates a difficult situation for cybersecurity professionals.
Defenders must protect systems against experienced criminals while also considering attackers who may have fewer technical skills but access to powerful automated tools.
Nevertheless, AI does not eliminate the need for expertise. Successful attacks still depend on access, opportunities and weaknesses in the targeted environment.
Why Traditional Cybersecurity Defenses May Not Be Enough
Many organizations already use firewalls, antivirus software and network monitoring systems.
These tools remain important, but security teams must adapt to attacks that move faster and involve more automation.
A security system that detects suspicious activity may not automatically prevent an intrusion.
Organizations need to identify threats, investigate alerts and respond before criminals gain greater access.
Faster Detection Is Becoming Essential
Traditional security investigations can involve several manual steps.
Security professionals may need to review network logs, examine suspicious files and identify unusual account activity.
AI-powered attacks can increase the volume and speed of suspicious operations.
This creates pressure on security teams to investigate alerts quickly.
Organizations should consider automated monitoring systems that can identify unusual behavior and help security professionals prioritize serious incidents.
Weak Passwords Remain a Major Problem
Despite advances in cybersecurity technology, weak passwords continue to create opportunities for criminals.
Reused passwords can expose several accounts when one service experiences a data breach.
Organizations should introduce stronger authentication requirements and encourage employees to use password managers.
Multi-factor authentication can provide another layer of protection.
However, users should also protect authentication methods from phishing and fraudulent verification requests.
Unpatched Software Creates Opportunities
Software vulnerabilities are another common entry point for attackers.
Companies sometimes delay updates because they fear interruptions or compatibility problems.
However, outdated systems can remain exposed to known security weaknesses.
Organizations should maintain an accurate inventory of internet-facing applications and prioritize important security updates.
The FBI’s recommendations concerning AI-assisted attacks emphasize stronger identity controls, application protection and attention to exposed systems.
Inc.com+1
What Businesses Should Do to Protect Their Systems
Businesses cannot eliminate every cyber risk, but they can reduce their exposure through consistent security practices.
The growing AI cyber threat makes preparation particularly important.
Here are several measures organizations should consider.
1. Strengthen identity verification
Businesses should require strong authentication for employees, administrators and third-party contractors.
Multi-factor authentication should be enabled wherever possible.
2. Protect sensitive credentials
API keys, passwords and access tokens should never be stored in public repositories or unsecured files.
Companies should regularly review permissions and replace compromised credentials.
3. Monitor unusual network activity
Security teams should investigate unexpected login attempts, unusual data transfers and suspicious administrative activity.
Automated monitoring can help identify patterns that deserve immediate attention.
4. Update software regularly
Organizations should apply security patches and remove unnecessary internet-facing services.
Older systems should receive additional protection when immediate replacement is not possible.
5. Prepare incident response plans
Businesses should establish clear procedures for responding to cyberattacks.
Employees should know whom to contact and how to report suspicious activity.
6. Secure third-party connections
Companies should review the security of vendors, software providers and business partners.
A weakness in one connected organization can create risks for others.
7. Train employees
Regular cybersecurity training can help workers recognize phishing attempts, deepfake scams and suspicious requests.
These steps are consistent with the basic security practices emphasized in recent FBI and industry guidance.
Inc.com+2
How Ordinary Internet Users Can Protect Themselves
Although major companies and government agencies face significant risks, ordinary internet users should also take precautions.
Personal accounts contain valuable information, including financial records, private messages, photographs and identity details.
Criminals may target these accounts through phishing, impersonation and credential theft.
The following steps can help reduce exposure.
Use a different strong password for every important account.
Enable multi-factor authentication.
Avoid clicking unexpected links in emails and text messages.
Never share one-time passwords with callers or unknown contacts.
Verify urgent financial requests through another communication channel.
Keep phones, computers and applications updated.
Avoid downloading software from unfamiliar websites.
Review bank transactions and account login notifications.
Back up important documents and photographs.
Report suspected online fraud to the appropriate authorities.
Users should also remember that AI-generated content can look and sound convincing.
A familiar voice or realistic video should not be treated as sufficient proof of someone’s identity.
If a message requests money, sensitive information or immediate account access, verify the request independently.
Could AI-Powered Hacking Become a National Security Threat?
The growing misuse of artificial intelligence has implications beyond individual businesses.
Cyberattacks against essential infrastructure could affect public services, economic activity and national security.
Electricity networks, water systems, transportation services and telecommunications infrastructure depend on interconnected digital technologies.
Disruptions to these systems could create consequences that extend far beyond the original victim.
The US government has already highlighted concerns involving AI-assisted cyber operations against industrial control systems.
These warnings underline the importance of protecting operational technology alongside traditional computer networks.
The Record from Recorded Future News+1
The Role of State-Sponsored Hackers
Another concern involves government-backed hacking groups.
State-sponsored actors may use cyber operations for espionage, intelligence collection or disruption.
AI could help these groups analyze large quantities of information and coordinate technical operations.
The challenge becomes more complicated when criminal groups and state-linked actors use similar tools.
Attribution can be difficult because investigators must establish who conducted an attack, what infrastructure was involved and whether the activity was directed by a government.
For this reason, cybersecurity agencies increasingly depend on information sharing with private companies and international partners.
Why International Cooperation Matters
Cybercrime does not respect national borders.
An attacker may operate from one country, use servers in another and target victims across several regions.
This makes international cooperation important.
Law enforcement agencies, technology companies and cybersecurity researchers need to exchange threat intelligence and coordinate investigations.
Cooperation can also help organizations identify malicious infrastructure and respond to attacks more effectively.
The Challenge of Controlling Powerful AI Tools
One of the biggest questions surrounding the AI cyber threat is how technology companies should manage powerful AI systems.
AI developers introduce safeguards to prevent their products from assisting harmful activities.
However, criminals may attempt to bypass these protections, use modified software or combine several different tools.
Open-source frameworks create additional challenges because their code may remain available through copies and modified versions even after the original developer removes a repository.
The ARTEX case illustrates this problem.
According to the FBI-related reporting, the framework’s original repository was removed after concerns about misuse emerged. However, copies and other versions continued circulating.
Inc.com+1
This highlights an important limitation of relying exclusively on removing a tool.
Once software has been distributed, controlling every copy can be extremely difficult.
AI Developers Have a Responsibility
Technology companies need to consider how their products could be misused.
Responsible development should include security testing, abuse monitoring and safeguards against harmful applications.
Companies should also cooperate with cybersecurity researchers when they discover vulnerabilities or suspicious activity.
At the same time, AI tools can strengthen cybersecurity defenses.
They can help security professionals investigate suspicious behavior, prioritize alerts and understand emerging threats.
The challenge is to encourage legitimate innovation without allowing criminals to exploit the same capabilities.
Can AI Also Help Defend Against Cyberattacks?
Despite the growing risks, artificial intelligence is not exclusively a tool for criminals.
Cybersecurity professionals are increasingly using AI to strengthen digital defenses.
AI-powered security systems can analyze large amounts of network information and identify suspicious patterns.
They can also help organizations investigate security incidents more efficiently.
Some important defensive applications include:
Threat detection: AI can identify unusual network activity and suspicious login behavior.
Fraud prevention: Financial institutions can use machine learning to identify potentially fraudulent transactions.
Malware analysis: Security researchers can use AI to examine suspicious files and understand malicious behavior.
Incident response: Automated systems can help security teams prioritize alerts and investigate possible breaches.
Vulnerability management: AI can help identify weaknesses that require attention.
However, AI-based defense systems are not perfect.
They can produce false alarms, overlook sophisticated threats or become vulnerable to manipulation.
Human oversight remains essential.
The most effective approach combines AI-powered security tools with experienced professionals, strong security policies and regular system updates.
What Happens Next in the AI Cybersecurity Battle?
The cybersecurity landscape is entering a period of significant change.
As AI systems become more capable, attackers and defenders will continue competing to use these technologies effectively.
Criminal groups may develop more sophisticated automation, while security companies work to improve detection and response capabilities.
The recent warnings involving ARTEX demonstrate that this is no longer simply a theoretical concern.
AI-assisted frameworks are already being investigated in connection with real cyber campaigns.
For businesses, the priority should be preparation rather than panic.
Organizations need to understand their digital infrastructure, protect sensitive information and establish effective response procedures.
Individuals should also improve their online security habits.
The warning from former FBI counterterrorism official Bassem Youseff reinforces a broader concern: artificial intelligence could make existing cyber threats faster, more scalable and more difficult to manage.
Ultimately, the technology itself is not the enemy. The challenge is preventing criminals from turning powerful digital tools into weapons.
As AI continues to evolve, cybersecurity will become an increasingly important responsibility for governments, businesses and internet users worldwide.
Frequently Asked Questions (FAQs)
1. What is the AI cyber threat?
The AI cyber threat refers to the misuse of artificial intelligence by cybercriminals to conduct attacks. These activities may include automated hacking, phishing, malware development, identity theft and data breaches.
2. Why are hackers weaponizing AI tools?
Hackers are using AI because it can automate repetitive tasks, analyze information quickly and help coordinate complex cyber operations. These capabilities can reduce the time and effort required to conduct certain attacks.
3. What did the retired FBI official warn about?
Former FBI counterterrorism unit chief Bassem Youseff warned that AI could significantly increase the speed and scale of cyberattacks. His comments highlighted the growing risks associated with automated hacking capabilities.
4. What is ARTEX in cybersecurity?
ARTEX is an AI-powered penetration-testing framework. Although designed around security testing, the FBI has warned that malicious actors have repurposed it to automate cyberattacks against organizations.
5. Can AI tools create malware?
AI tools can potentially assist criminals in developing or modifying malicious code. They may also help explain programming techniques and automate certain activities. However, safeguards and technical limitations vary between AI systems.
6. Which industries are most vulnerable to AI-powered cyberattacks?
Financial services, healthcare, government, telecommunications, energy and technology companies face significant cybersecurity risks. Organizations managing sensitive information or essential infrastructure require particularly strong protection.
7. Can AI-generated deepfakes be used for cybercrime?
Yes. Criminals can use AI-generated voices, images and videos to impersonate trusted individuals. These techniques may support financial scams, identity fraud and attempts to bypass verification systems.
8. How can businesses protect themselves from AI hackers?
Businesses should use multi-factor authentication, update software regularly, secure sensitive credentials, monitor network activity and train employees to recognize phishing attempts.
9. Can ordinary people become victims of AI-powered cybercrime?
Yes. Individuals may face AI-assisted phishing, fake customer support calls, deepfake impersonation and financial scams. Strong passwords and careful verification of suspicious requests can reduce these risks.
10. Will AI make cyberattacks more dangerous in the future?
AI could make some cyberattacks faster, more automated and easier to scale. However, stronger defensive technologies and improved cybersecurity practices can also help organizations respond to emerging threats.
About the Author