A wave of technology outages across the United States has raised serious concerns about cybersecurity, national infrastructure and the possibility of coordinated foreign attacks. From disrupted airline operations to banking problems and major technology service failures, Americans have experienced an unusual series of digital interruptions.
However, senior US government officials say there is currently no evidence that these incidents are connected or caused by coordinated cyberattacks.
During a congressional hearing on November 18, 2026, top national security officials addressed growing public anxiety. They explained that the recent disruptions appear to involve separate technical failures, maintenance activities and system upgrades rather than hostile actions by foreign governments or cybercriminal organizations.
The reassurances come after disruptions affected Microsoft services, the Federal Aviation Administration (FAA), major banks, United Airlines and even internal communications systems at the National Security Agency (NSA).
Despite those explanations, questions remain about why so many critical systems experienced problems within such a short period.
The situation has renewed discussions about America’s dependence on aging technology, cybersecurity preparedness and the growing risks associated with interconnected digital infrastructure.
US Cyberattack Fears Grow Following Multiple Technology Outages
The recent wave of outages has attracted national attention because several important services experienced disruptions almost simultaneously.
For ordinary Americans, the problems created confusion and inconvenience. Travelers faced flight disruptions, banking customers encountered transaction delays, and businesses struggled with technology services they depend on every day.
The timing also raised concerns about whether a foreign adversary could be testing weaknesses in American infrastructure.
However, officials have repeatedly rejected the suggestion that the incidents represent a coordinated attack.
Director of National Intelligence Jay Clayton told lawmakers that investigators had examined the incidents with government agencies and private-sector cybersecurity specialists.
He explained that the disruptions were separate service outages associated with maintenance and technical changes.
According to Clayton, investigators had not identified evidence of a coordinated or state-sponsored operation.
Homeland Security Secretary Markwayne Mullin also attempted to reassure Americans. He said federal authorities had found no indication connecting the outages to malicious activity.
Mullin expressed strong confidence that foreign adversaries were not responsible for the recent disruptions.
Nevertheless, the number of affected services has made the situation difficult to ignore.
National Security Officials Address Cyberattack Concerns
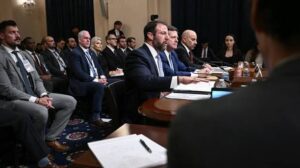
The House Homeland Security Committee hearing on November 18 became an important moment in the government’s response to the growing concerns.
Several senior officials appeared before lawmakers to discuss threats facing the United States.
Those officials included:
- Jay Clayton: Director of National Intelligence.
- Markwayne Mullin: Secretary of Homeland Security.
- Christopher Raia: FBI Deputy Director.
Their testimony focused on the recent technology failures, possible foreign threats and the government’s ability to protect critical infrastructure.
Clayton emphasized that intelligence agencies had investigated whether the incidents were connected.
He said officials found no evidence supporting the theory of a coordinated attack by a foreign government.
Mullin similarly explained that federal authorities were working with private companies to understand the disruptions.
He also acknowledged that the number of outages occurring within such a short period was unusual.
FBI Deputy Director Christopher Raia confirmed that cybersecurity specialists had been involved in examining the incidents.
He said investigators had found no indication of malicious cyber activity connected to the outages.
However, Raia stressed that the FBI would continue cooperating with private-sector partners.
This approach reflects the government’s position: officials do not currently believe the outages represent a coordinated cyberattack, but they are not abandoning investigations.
FAA Outage Causes Nationwide Flight Disruptions
One of the most significant incidents involved the Federal Aviation Administration.
On November 13, 2026, the FAA issued a nationwide ground stop that disrupted air travel across the United States.
The incident created major problems for airlines, passengers and airport operations.
According to officials, the disruption involved telecommunications infrastructure at an FAA facility in Arkansas.
The problem emerged during work to replace outdated copper communications lines with modern fiber-optic connections.
During the transition, a router began sending excessive data across the network.
This overwhelmed other network equipment and disrupted communications.
As a result, the FAA temporarily halted flights while authorities worked to restore normal operations.
The disruption had significant consequences for travelers. Reports indicated that more than 18,000 flights were canceled over the following three days.
The incident raised questions about the reliability of aviation infrastructure.
Air traffic control depends on communication systems that must operate continuously and accurately.
Even a relatively small technical failure can create widespread consequences when it affects systems responsible for coordinating aircraft movements.
FAA officials said they had found no evidence of malicious activity behind the disruption.
Nevertheless, the incident demonstrated how aging infrastructure and complicated technology upgrades can affect essential public services.
Microsoft Outage Adds to America’s Technology Concerns
Another major disruption involved Microsoft’s cloud and productivity services.
On November 12, Microsoft 365 applications experienced a significant outage that affected users across multiple countries.
Services such as Outlook and Teams became unavailable or experienced performance problems.
The disruption affected businesses, government organizations and individuals who rely on Microsoft’s cloud infrastructure for everyday communication.
Microsoft later explained that technical problems involving its networking gateway contributed to the incident.
The company’s investigation identified a software defect and problems involving server resources.
Microsoft said the incident was not caused by a cyberattack.
The outage highlighted the importance of cloud computing in modern business operations.
Millions of users depend on cloud platforms to exchange information, organize meetings, store documents and manage essential workflows.
When these services experience disruptions, the consequences can extend far beyond individual computers.
Businesses may lose access to communication tools, employees may struggle to complete assignments, and customers may experience delays.
The Microsoft incident therefore became another important part of the wider discussion about US cyberattack fears.
Although officials and companies rejected the hacking theory, the disruption demonstrated how much modern organizations depend on a relatively small number of major technology providers.
Banking Disruptions Raise Questions About Financial Security
The financial sector also experienced problems during the recent series of outages.
JPMorgan Chase, one of America’s largest financial institutions, reported technical issues that affected banking services.
Customers experienced delays and difficulties involving online transactions.
Other financial services also faced disruptions.
The situation attracted attention because banking systems are essential to the country’s economy.
Consumers depend on digital banking for payments, transfers, account management and everyday purchases.
Businesses also require reliable financial platforms to process transactions and manage operations.
Even temporary interruptions can create uncertainty among customers.
However, reports attributed the Chase disruption to a software bug rather than malicious activity.
Officials said they had found no evidence connecting the banking problems to a coordinated cyberattack.
The incident nevertheless highlighted an important issue.
Financial institutions must constantly update their technology while protecting systems that handle sensitive customer information.
Software improvements can strengthen security, but poorly managed changes may also create unexpected technical problems.
This balance remains a major challenge for the financial industry.
NSA Communications Disruption Raises National Security Questions
Perhaps the most sensitive incident involved the National Security Agency.
On November 17, reports emerged that an internal NSA communications network had experienced temporary degradation during scheduled maintenance.
The agency confirmed that some internal systems were affected.
However, it emphasized that mission-critical capabilities remained operational.
The incident attracted attention because the NSA plays a central role in America’s intelligence and cybersecurity operations.
Any disruption involving its internal communications infrastructure naturally raises questions about national security.
Lawmakers wanted additional information about the circumstances surrounding the incident.
Some questioned whether the problem was connected to software updates or maintenance procedures.
Nevertheless, intelligence officials maintained that they had found no evidence of a cyberattack.
The NSA situation demonstrates why government agencies must maintain strong backup systems.
Sensitive communications networks need reliable infrastructure, regular testing and effective recovery procedures.
Even when an outage does not involve an outside attacker, it can expose weaknesses that deserve attention.
Why Officials Believe the Outages Are Not Connected
The central argument presented by US officials is that the incidents have different technical explanations.
Although the timing appears unusual, investigators have not identified a common attacker or coordinated operation.
Several disruptions involved maintenance activities, software bugs, network configurations and outdated equipment.
These problems can occur independently.
For example, an airline communications failure does not necessarily have the same technical cause as a banking software problem.
Similarly, a cloud service outage may result from server configuration issues rather than an attempt to gain unauthorized access.
Officials say they have examined the available information and found no evidence linking the incidents.
National Security Adviser Marco Rubio also emphasized that the government had no indication that the disruptions were connected.
The administration’s position is that companies and government agencies are upgrading systems and addressing vulnerabilities.
Those improvements can temporarily disrupt services, particularly when older infrastructure struggles to support new technology.
However, the distinction between an absence of evidence and absolute proof is important.
Investigations can develop as new information becomes available.
Therefore, officials’ statements should be understood as their current assessment rather than a guarantee that every possible cybersecurity risk has disappeared.
Aging Technology Creates New Risks for Critical Infrastructure
One of the biggest lessons from the recent outages concerns America’s aging digital infrastructure.
Many essential services depend on technology systems developed years or even decades ago.
These systems often support modern applications, cloud platforms and increasingly complicated digital networks.
Integrating newer technology with older equipment can create unexpected compatibility problems.
For example, an upgrade designed to improve performance may place additional pressure on legacy hardware.
A network designed for a particular amount of traffic may struggle when new services increase demand.
Likewise, a configuration change can affect several connected systems if the equipment depends on shared infrastructure.
These problems are not necessarily cybersecurity incidents.
However, they can create weaknesses that malicious actors might attempt to exploit.
This is why experts continue to emphasize the importance of modernization.
Government agencies and private companies need to identify outdated systems, improve network monitoring and test upgrades before deploying them widely.
The recent disruptions show that infrastructure reliability is just as important as cybersecurity protection.
Artificial Intelligence Adds Another Layer to Cybersecurity Concerns
Artificial intelligence has also become part of the discussion surrounding the recent technology failures.
AI tools can help cybersecurity researchers identify vulnerabilities more quickly.
This allows organizations to discover weaknesses that might otherwise remain unnoticed for years.
However, identifying vulnerabilities creates pressure to fix them.
When multiple organizations attempt major upgrades at the same time, technical problems can emerge.
Jay Clayton suggested that the increased ability to identify vulnerabilities has encouraged institutions to patch and upgrade systems on a larger scale.
These changes are important for long-term security.
Nevertheless, rushed upgrades can introduce configuration mistakes, software incompatibilities and unexpected system failures.
AI also creates challenges for defenders because sophisticated cybercriminals can use automated tools to improve their operations.
This means organizations must prepare for both sides of the technology revolution.
They need to use AI to strengthen security while ensuring that automated changes do not create additional operational risks.
The current outages have not been established as AI-driven attacks.
However, they have renewed debate about how artificial intelligence is changing the cybersecurity environment.
Lawmakers Demand Greater Transparency
Despite reassurances from federal officials, some lawmakers remain concerned about the limited information available to the public.
They argue that Americans deserve clear explanations when essential services experience widespread disruptions.
The concern is understandable.
When banking, aviation, communications and government technology encounter problems within days, people naturally want to know whether there is a larger issue.
Senators and cybersecurity experts have emphasized the importance of transparency.
They want companies and government agencies to explain what failed, how the incidents were investigated and what steps will prevent similar problems.
Clear communication is particularly important during cybersecurity scares.
Conflicting explanations can increase public anxiety and encourage misinformation.
Organizations should distinguish between confirmed technical causes, ongoing investigations and issues that remain unresolved.
They should also explain whether customer information, financial data or sensitive government systems were affected.
Public confidence depends not only on preventing attacks but also on communicating honestly when technology fails.
Could Future Outages Create a Bigger National Security Problem?
Although officials have rejected claims of a coordinated cyberattack, the recent incidents have highlighted vulnerabilities that deserve serious attention.
America’s critical infrastructure relies on complex digital systems.
These systems support transportation, banking, healthcare, energy, communications and national security.
A disruption affecting one important service can create consequences across several industries.
For example, an aviation communications failure can affect passengers, airline schedules, airport operations and supply chains.
Similarly, a banking outage can delay business payments and create uncertainty for customers.
The growing dependence on connected technology makes resilience increasingly important.
Experts argue that organizations should prepare for both accidental failures and deliberate attacks.
That preparation includes maintaining backup systems, improving cybersecurity monitoring and developing effective recovery plans.
It also requires regular testing to identify weaknesses before they cause major disruptions.
The recent outages may have resulted from separate technical failures, but they demonstrate why infrastructure modernization cannot be delayed indefinitely.
What Happens Next in the US Cybersecurity Investigation?
Federal authorities are expected to continue monitoring potential threats while working with private companies.
The FBI, intelligence agencies and Department of Homeland Security have an important role in identifying malicious activity and protecting critical infrastructure.
Companies affected by the outages must also examine their systems and explain what went wrong.
The priority is to restore reliability while ensuring that upgrades do not introduce additional vulnerabilities.
For government agencies, this means improving coordination between cybersecurity specialists, infrastructure operators and private technology providers.
For businesses, it means reviewing software deployment procedures, testing backup systems and improving incident response plans.
The public should also expect continued discussion about America’s dependence on aging technology.
The recent disruptions have demonstrated that cybersecurity is not limited to preventing hackers from entering computer networks.
It also involves ensuring that essential systems remain available, stable and capable of recovering when something goes wrong.
Conclusion: US Cyberattack Fears Remain Despite Official Reassurances
The recent wave of technology outages has placed US cybersecurity and infrastructure reliability under intense scrutiny.
Major disruptions involving Microsoft, the FAA, banking services, United Airlines and the NSA have raised questions about whether America is facing a broader digital threat.
However, senior national security officials say investigations have found no evidence of a coordinated cyberattack or foreign government involvement.
Instead, the incidents appear to involve separate technical failures, maintenance activities, software problems and infrastructure upgrades.
That assessment offers some reassurance, but it does not eliminate the need for stronger security and modernization.
The outages have exposed how dependent Americans are on interconnected digital systems.
They have also demonstrated that technical failures can create serious consequences even when no hacker is involved.
Ultimately, protecting America’s digital infrastructure requires more than ruling out cyberattacks. It requires reliable technology, transparent investigations, stronger backup systems and continuous cooperation between government agencies and private companies.
The central question now is whether the United States can modernize its aging infrastructure quickly enough to prevent another wave of disruptive outages.
Frequently Asked Questions (FAQs)
1. Are the recent US technology outages caused by cyberattacks?
US national security officials say there is currently no evidence that the recent outages were caused by coordinated cyberattacks. Investigators believe the incidents involved separate technical failures, maintenance activities and software problems.
2. Which US services were affected by the recent outages?
The disruptions affected Microsoft services, Federal Aviation Administration systems, United Airlines operations, JPMorgan Chase banking services, Apple services and an internal communications network at the National Security Agency.
3. What did US intelligence officials say about the outages?
Director of National Intelligence Jay Clayton told Congress that the outages were separate service disruptions associated with maintenance and technical changes. He said investigators found no evidence of a coordinated or state-sponsored attack.
4. Did the FAA outage affect flights across America?
Yes. On November 13, 2026, the FAA issued a nationwide ground stop following telecommunications problems. The disruption contributed to widespread flight cancellations and delays.
5. Was the Microsoft outage caused by hackers?
Microsoft said its November 12 service disruption resulted from technical problems involving its networking gateway. Its investigation identified software and server-related issues rather than a cyberattack.
6. Why are Americans worried about a possible cyberattack?
The concerns increased because several important services experienced outages within a short period. The affected sectors included aviation, banking, cloud computing and national security.
7. What role does aging technology play in the outages?
Older infrastructure may struggle to support modern applications and increased network traffic. Software updates and system upgrades can also create compatibility problems when organizations rely on outdated equipment.
8. Is artificial intelligence responsible for the recent outages?
Officials have not established that AI caused the recent outages. However, artificial intelligence can help identify software vulnerabilities and accelerate cybersecurity upgrades, which may create additional technical challenges.
9. Are US government agencies investigating the incidents?
Yes. The FBI, Department of Homeland Security and intelligence agencies have been involved in examining potential threats and coordinating with private-sector organizations.
10. Should Americans be concerned about future cyberattacks?
Cybersecurity remains an important national security concern. Although officials have found no evidence connecting the recent outages to a coordinated attack, organizations must continue improving infrastructure, monitoring threats and preparing for potential disruptions.
About the Author