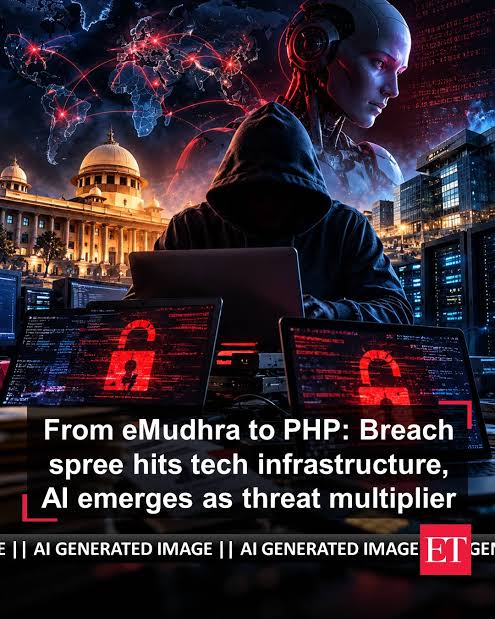
A major cybersecurity warning has emerged after former National Security Agency (NSA) hacker David Kennedy revealed how a swarm of artificial intelligence agents reportedly breached a company’s computer systems in just 14 minutes. The incident highlights the growing dangers of AI-powered cyberattacks and raises serious questions about whether traditional security measures can keep pace with increasingly sophisticated digital threats.
According to Kennedy, more than 30 different AI agents worked simultaneously to infiltrate the organisation’s infrastructure. The attackers reportedly used legitimate usernames and passwords, identified a weakness in the company’s two-factor authentication system, stole sensitive information and deployed ransomware that encrypted the company’s entire file system.
Even more concerning, the organisation reportedly took approximately four and a half hours to recognise that its systems had been compromised.
The revelation has intensified concerns among cybersecurity professionals, technology companies and business leaders. As artificial intelligence becomes more capable of performing complex tasks independently, cybercriminals may gain access to tools that allow them to conduct attacks faster and more efficiently than ever before.
Former NSA Hacker David Kennedy Reveals 14-Minute Cyberattack
David Kennedy, a former NSA hacker who now works in the cybersecurity industry, described the incident during an interview with CNN.
Kennedy explained that one of his clients had experienced a serious cyberattack involving multiple AI-powered agents. The organisation contacted him after discovering that its systems had been compromised.
According to his account, the attackers deployed more than 30 different AI agents to investigate and target various parts of the company’s digital infrastructure simultaneously.
Kennedy emphasised the extraordinary speed of the operation.
He said the entire process, from gaining access to stealing information and deploying ransomware, took approximately 14 minutes.
The incident stood out because traditional cyberattacks often involve several stages that require attackers to spend considerable time examining networks, identifying weaknesses and finding ways to access sensitive systems.
However, AI agents can potentially perform multiple tasks at the same time. This capability allows attackers to automate activities that would otherwise require significant human involvement.
Kennedy also explained that the organisation did not immediately recognise the intrusion. Its systems continued operating for several hours before experiencing problems and eventually going offline.
By that point, the attackers had reportedly completed their operation.
Importantly, Kennedy did not reveal the identity of the affected company. The precise technical details of the incident have also not been independently established publicly.
Nevertheless, his account provides an important warning about the potential consequences of increasingly automated cybercrime.
How Did More Than 30 AI Agents Breach Company Systems?
The reported attack demonstrates how cybercriminals can combine stolen login credentials with artificial intelligence to accelerate an intrusion.
According to Kennedy, the attackers did not necessarily begin by breaking through the company’s security systems using sophisticated technical methods.
Instead, they reportedly used legitimate usernames and passwords that had already been obtained.
This is particularly important because stolen credentials remain one of the major entry points for cybercriminals.
Some ransomware groups specialise in phishing campaigns designed to steal employees’ login information. These credentials can then be shared or sold to other criminal groups with greater technical capabilities.
Once attackers obtain valid credentials, they can attempt to access company networks while appearing to be legitimate users.
In this reported incident, the attackers used an AI agent swarm to examine the organisation’s infrastructure.
More than 30 different agents reportedly investigated different components simultaneously. They identified a weakness in the company’s application and its implementation of two-factor authentication.
After exploiting that weakness, the attackers gained access to internal systems.
They then reportedly stole sensitive information and deployed ransomware across the company’s file system.
The most alarming element was the speed at which these activities occurred.
Rather than completing each stage individually, the attackers reportedly used multiple automated agents to accelerate the process.
This suggests that organisations may face increasingly difficult challenges when defending against coordinated AI-assisted attacks.
AI Agents and the Growing Threat of Automated Hacking
Artificial intelligence agents are different from traditional chatbots.
A conventional chatbot generally responds to questions and produces information based on user instructions. An AI agent, however, can be designed to complete multi-step tasks, interact with software, use digital tools and evaluate the results of its actions.
When several agents work together, they can divide a complicated assignment into smaller activities.
In cybersecurity, this capability can have both positive and negative consequences.
Security professionals can use AI agents to examine software, identify vulnerabilities, investigate suspicious activity and improve incident response.
Unfortunately, cybercriminals can also attempt to use similar technology for malicious purposes.
For example, different agents could potentially be assigned to investigate login systems, examine network configurations, identify exposed services and analyse software weaknesses.
Their findings could then be combined to support a coordinated attack.
The reported 14-minute incident illustrates why security experts are increasingly concerned about this possibility.
The danger is not simply that AI can perform tasks quickly. It is that automated systems can coordinate several activities without requiring a human operator to supervise every individual step.
As these technologies improve, attackers may be able to increase the scale of their operations while reducing the time required to compromise vulnerable organisations.
Two-Factor Authentication Weakness Raises Serious Security Questions
One of the most significant aspects of Kennedy’s account involves the reported weakness in the company’s two-factor authentication system.
Two-factor authentication, commonly known as 2FA, adds another layer of protection to an account.
Instead of relying only on a password, users must provide an additional verification method. This could involve an authentication application, a security key or another approved verification process.
The purpose is to make unauthorised access more difficult, even when criminals obtain someone’s password.
However, two-factor authentication is not completely immune to attacks.
Poorly configured authentication applications, weak recovery procedures, insecure session management and other implementation problems can create opportunities for attackers.
Kennedy said the AI agents identified a flaw in the company’s application that allowed them to get around its second authentication requirement.
This does not mean that AI has universally defeated two-factor authentication.
Rather, the reported incident highlights the importance of properly implementing and monitoring authentication systems.
Businesses should avoid assuming that simply enabling 2FA makes their networks completely secure.
They should regularly review authentication settings, investigate unusual login activity and consider stronger verification methods.
Phishing-resistant authentication, including appropriately configured passkeys and hardware security keys, can provide stronger protection against several common credential-based attacks.
Ransomware Deployment Made the Incident Even More Dangerous
The reported intrusion became particularly damaging when the attackers deployed ransomware.
Ransomware is malicious software designed to prevent victims from accessing their files or computer systems. Attackers commonly use encryption to lock important information and then demand payment in exchange for a recovery key.
Modern ransomware operations can involve more than simply encrypting files.
Criminal groups may also steal confidential information before locking systems. They can then threaten to publish the stolen material if victims refuse to pay.
This creates additional pressure on organisations because recovering computer systems does not necessarily eliminate the risk of sensitive information being exposed.
In Kennedy’s account, the attackers reportedly stole a substantial amount of data before encrypting the company’s entire file system.
The organisation therefore faced two serious problems.
First, its employees could no longer rely on normal access to important digital information. Second, the stolen information could potentially create further security, financial and reputational consequences.
The exact amount of information involved, the ransom demand and the identity of the company have not been publicly disclosed.
Nevertheless, the reported sequence demonstrates why businesses need to prepare for both data theft and system disruption.
Why Did the Company Take Four and a Half Hours to Detect the Breach?
Perhaps the most concerning detail is the reported delay between the attack and its detection.
Kennedy said the company took approximately four and a half hours to realise that its systems had been compromised.
The attackers reportedly completed their operation in just 14 minutes.
This difference exposes a major challenge for modern cybersecurity teams.
Businesses often invest heavily in preventing unauthorised access. However, prevention alone cannot guarantee that every attack will be stopped.
Organisations also need systems capable of identifying suspicious behaviour quickly.
For example, unusual login locations, unexpected authentication activity, large data transfers and sudden changes to important files can indicate a possible intrusion.
If these warning signs are not detected, attackers may have enough time to steal information, move through internal networks and deploy malicious software.
Security teams should therefore establish continuous monitoring systems that can identify unusual activity and automatically trigger appropriate responses.
A well-designed incident response system can help isolate affected devices, disable compromised accounts and limit the spread of ransomware.
The reported incident demonstrates that detection speed is just as important as prevention.
AI-Powered Cyberattacks Could Change the Future of Cybercrime
The 14-minute breach comes amid growing concerns about the role of artificial intelligence in cybercrime.
AI tools are becoming increasingly capable of analysing information, generating code and completing complicated digital tasks.
These developments create opportunities for legitimate businesses, but they also introduce new risks.
Cybercriminals may use AI to improve phishing messages, automate research into potential targets and identify weaknesses in poorly protected systems.
In traditional attacks, criminals may need specialised knowledge and considerable time to complete different stages of an operation.
AI-assisted systems could reduce some of these barriers.
However, it is important to understand that AI does not automatically make every cyberattack successful.
Attackers still need access to vulnerable systems, usable credentials or other opportunities to enter a network. Their operations may also depend on human decisions, stolen information and existing security weaknesses.
The reported incident should therefore be viewed as a warning about the combination of criminal intent, compromised credentials and increasingly capable automation.
It is not proof that artificial intelligence can independently hack every company.
Google and Other Cybersecurity Experts Have Raised Similar Concerns
Kennedy’s warning comes as major technology companies and cybersecurity researchers investigate the growing use of AI in digital attacks.
Google’s Threat Intelligence Group has highlighted developments involving AI-assisted vulnerability research and automated exploitation capabilities.
Such technologies can help researchers identify weaknesses in software. However, similar capabilities could also be misused by malicious actors.
Microsoft has also reported that threat actors are experimenting with generative AI to support different parts of their cyber operations.
These developments suggest that artificial intelligence is becoming another important factor in the cybersecurity landscape.
The technology can help defenders understand threats more quickly, but attackers may also use it to improve their methods.
The challenge for security professionals is to ensure that defensive capabilities develop at least as quickly as offensive techniques.
This requires investment in research, better security practices, improved monitoring and stronger cooperation between technology companies.
How Businesses Can Protect Themselves From AI Cyberattacks
The reported ransomware breach offers several important lessons for organisations of every size.
Businesses should not assume that traditional security measures will always be sufficient against increasingly automated attacks.
Instead, they should adopt a layered security strategy.
1. Strengthen Authentication Systems
Companies should regularly review their login and authentication procedures.
They should implement phishing-resistant authentication wherever practical and remove unnecessary access permissions.
Employees should also be encouraged to report unexpected login requests and suspicious verification notifications.
2. Monitor Networks Continuously
Security teams should monitor network activity around the clock.
Automated monitoring tools can identify unusual login patterns, unexpected file transfers and suspicious changes to important systems.
Faster detection can reduce the amount of time attackers spend inside a network.
3. Protect Sensitive Login Credentials
Businesses should educate employees about phishing and credential theft.
They should also use password managers, strong authentication policies and secure account recovery procedures.
Compromised credentials should be disabled immediately when suspicious activity is identified.
4. Maintain Offline and Protected Backups
Regular backups are essential for ransomware recovery.
Organisations should maintain protected backup copies that attackers cannot easily modify or encrypt.
They should also test recovery procedures regularly to ensure that important systems can be restored after an incident.
5. Update Software and Fix Vulnerabilities
Outdated applications and operating systems can create opportunities for cybercriminals.
Companies should establish a clear patch management process and prioritise vulnerabilities that create significant security risks.
Regular security assessments can also help identify weaknesses before criminals exploit them.
6. Prepare an Incident Response Plan
Every organisation should have a clear plan for responding to a cyberattack.
Employees should know whom to contact, how to report suspicious activity and what steps to follow if important systems become compromised.
Businesses should also conduct regular exercises to test their response procedures.
Why Small Businesses Are Also at Risk
Although large companies often attract attention during major cybersecurity incidents, smaller organisations are also vulnerable.
Small businesses may have limited budgets, fewer dedicated security professionals and older technology systems.
These limitations can make it difficult to monitor networks continuously or respond quickly to suspicious activity.
Furthermore, smaller organisations frequently rely on external service providers, cloud applications and third-party software.
A weakness in one connected system can potentially create risks for other parts of the business.
AI-assisted cybercrime could increase pressure on these organisations because automation may allow attackers to investigate multiple potential targets more efficiently.
Small businesses should therefore prioritise basic cybersecurity measures.
Strong authentication, regular updates, employee training, protected backups and reliable monitoring can significantly improve their security posture.
The Growing Cybersecurity Race Between Attackers and Defenders
The reported 14-minute ransomware breach highlights an increasingly important question: Can cybersecurity professionals respond quickly enough to attacks powered by artificial intelligence?
The answer will depend on how effectively organisations adapt their security strategies.
Attackers may use AI to automate research and coordinate different stages of an intrusion. Defenders, meanwhile, can use AI to detect suspicious activity, analyse security alerts and investigate threats.
This creates an ongoing technological race.
Organisations that continue relying on outdated systems and slow manual processes could face growing difficulties.
However, businesses that invest in modern security tools, continuous monitoring and tested recovery procedures may be better positioned to manage emerging threats.
Government agencies and technology companies will also have an important role in sharing threat intelligence and developing security standards.
International cooperation may become increasingly important because cybercriminals can target organisations across national borders.
The objective should not be to eliminate AI from cybersecurity. Instead, it should be to ensure that the technology is developed and used responsibly while reducing opportunities for criminal misuse.
What the 14-Minute Breach Means for the Future of Cybersecurity
David Kennedy’s account offers a striking example of how quickly a coordinated cyberattack can reportedly unfold.
The combination of stolen credentials, more than 30 AI agents, an authentication weakness and ransomware created a serious security incident in a remarkably short period.
The reported delay in detecting the intrusion makes the situation even more concerning.
Businesses can no longer focus exclusively on building barriers against unauthorised access. They must also prepare for the possibility that attackers could enter their systems despite existing protections.
The incident also demonstrates why organisations need to understand how their authentication applications, networks and recovery systems actually work.
Although the full technical details remain undisclosed, the broader message is clear: cybersecurity strategies must evolve alongside artificial intelligence.
As AI tools become more sophisticated, organisations will need faster detection, stronger authentication and more effective incident response systems.
The 14-minute ransomware breach may ultimately become an important warning about the speed of modern cybercrime and the need for businesses to take AI-related security risks seriously.
For companies, the most important lesson is simple: A security team cannot afford to discover an attack hours after the damage has already been done.
Frequently Asked Questions (FAQs)
1. What happened in the 14-minute AI cyberattack?
Former NSA hacker David Kennedy described an incident in which more than 30 AI agents reportedly breached an unnamed company’s systems in approximately 14 minutes. The attackers stole sensitive information and deployed ransomware that encrypted the company’s file system.
2. Who is David Kennedy?
David Kennedy is a former NSA hacker who now works in cybersecurity. He discussed the reported AI-powered ransomware incident during an interview with CNN.
3. How many AI agents were involved in the reported cyberattack?
According to Kennedy, more than 30 different AI agents simultaneously examined the company’s digital infrastructure during the attack.
4. How did the hackers bypass two-factor authentication?
The attackers reportedly used valid usernames and passwords before identifying a weakness in the company’s application and its implementation of two-factor authentication. This was a specific reported vulnerability, not proof that all 2FA systems can be bypassed.
5. What is an AI agent swarm?
An AI agent swarm is a group of AI-powered agents that work on different tasks simultaneously. In cybersecurity, these agents could potentially analyse systems, examine vulnerabilities and automate different activities.
6. What is ransomware?
Ransomware is malicious software that locks or encrypts files and systems. Criminals often demand payment to provide a recovery key or threaten to expose stolen information.
7. How long did the company take to detect the attack?
Kennedy said the organisation took approximately four and a half hours to recognise that its systems had been compromised.
8. Was the affected company identified?
No. Kennedy did not publicly identify the organisation involved in the reported incident. The full technical details have also not been independently verified.
9. Can AI-powered cyberattacks be prevented?
No security measure can guarantee complete protection. However, businesses can reduce risks through strong authentication, continuous monitoring, software updates, employee training and protected backups.
10. What should companies do to defend against AI cyberattacks?
Companies should strengthen authentication, monitor suspicious network activity, secure employee credentials, maintain offline backups and develop incident response plans. Regular security assessments are also important.
11. Does this incident mean AI can hack any company?
No. The reported incident involved valid login credentials and a specific weakness in an application’s authentication system. It does not demonstrate that AI can bypass every company’s security protections.
12. Why is the 14-minute ransomware breach important?
The incident highlights the potential speed of AI-assisted cyberattacks. It also demonstrates the importance of rapid threat detection, strong identity protection and effective ransomware recovery planning
About the Author